

Mobile devices
Mobile device management for Apple and Android
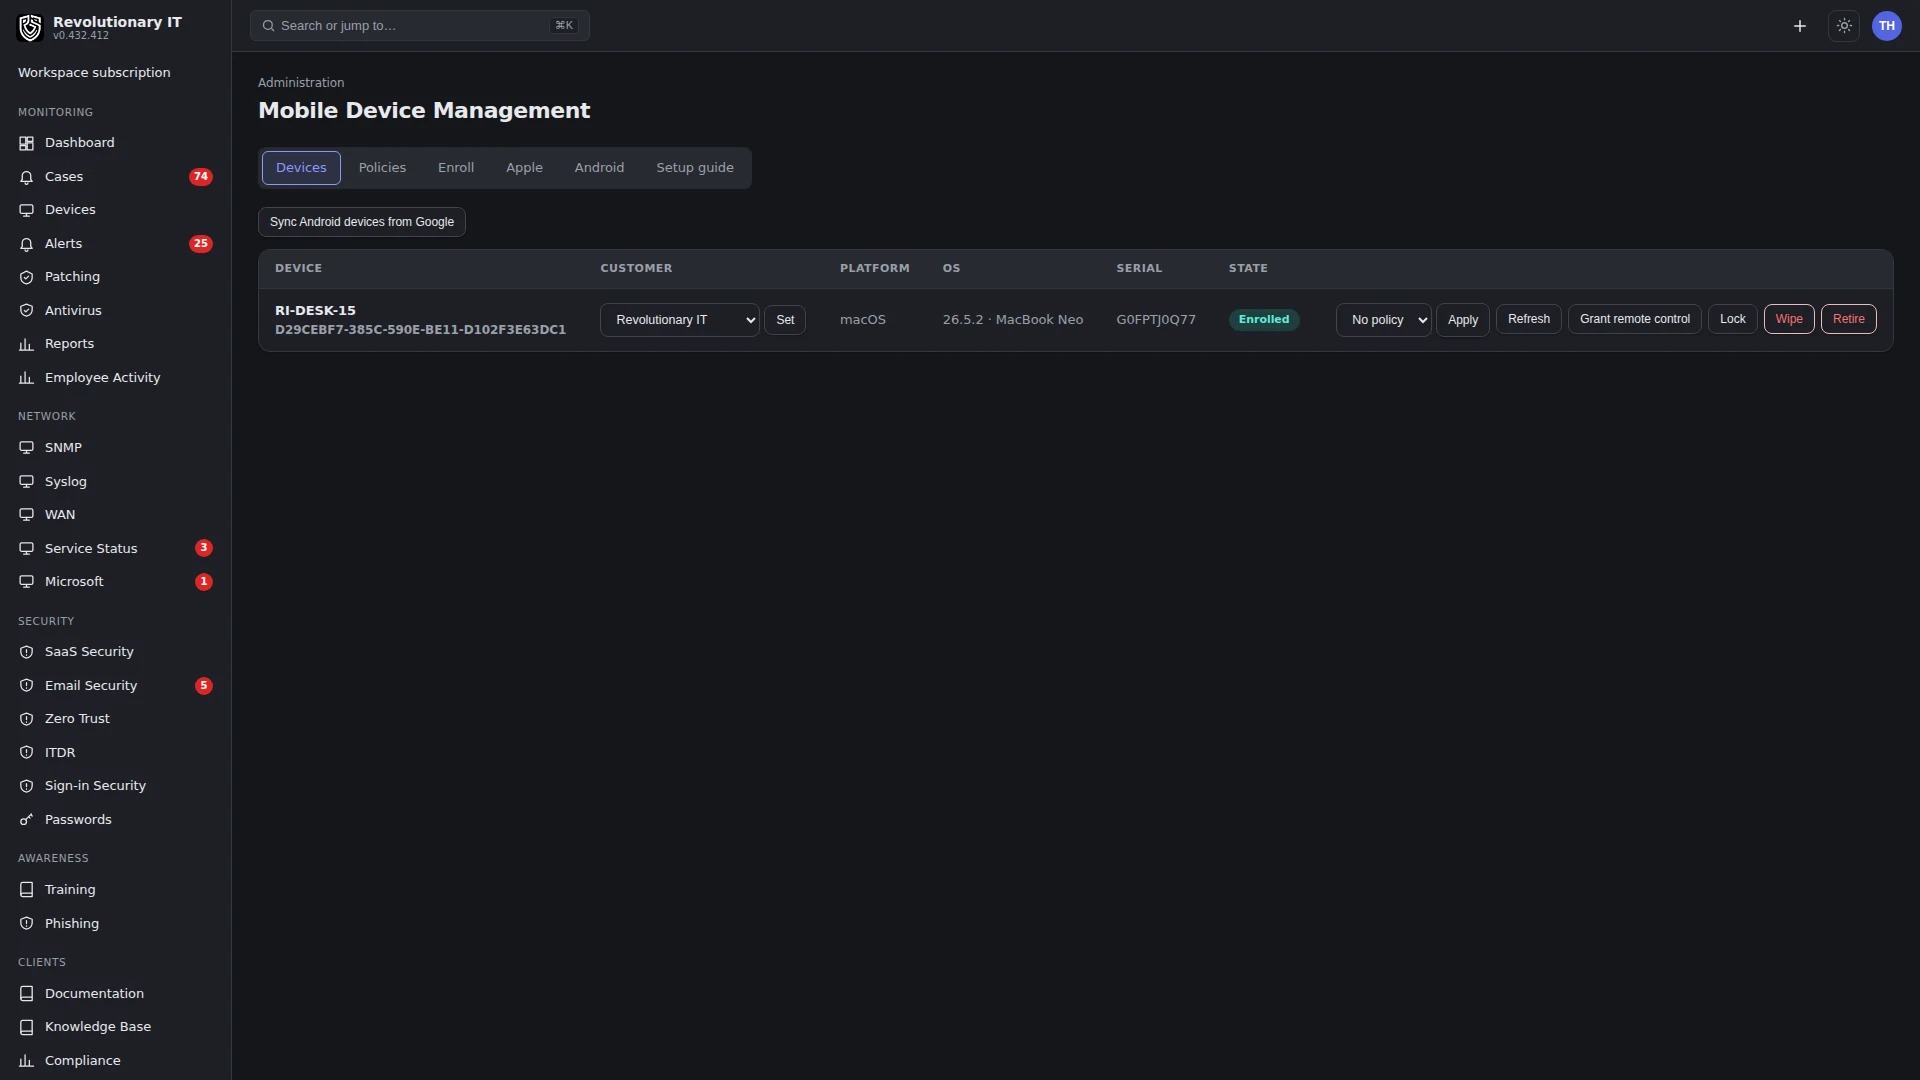
Manage iPhones, iPads, Macs and Android devices through the workspace MDM area. Apple and Google use separate enrollment and policy paths. Current deployment evidence confirms a managed Mac; Android requires a Google connection and device verification before customer rollout.
What it does
Enroll, apply policy, act when a device is lost.
01 / APPLE
Apple enrollment.
Manual profiles for iOS, iPadOS and macOS. Devices check in over the MDM protocol; Apple push notifications wake them to fetch commands.
02 / APPLE
Apple profiles.
Passcode, restriction and Wi-Fi profiles pushed to enrolled devices.
03 / APPLE
Apple actions.
Request inventory refresh, lock or erase. Queuing a command is separate from the device completing it; there is no Apple restart control here.
04 / ANDROID
Android enrollment.
Google-issued code and QR after enterprise binding, with the selected AMAPI policy pushed before token creation. Provisioning mode depends on the device setup flow.
05 / ANDROID
Android actions.
Request lock, reboot or wipe through Google. Supported actions and wipe scope depend on ownership and device mode; provider acceptance is not completion.
06 / PORTAL
Visible to the customer.
Assigned, non-retired devices appear read-only in the customer portal. After Android sync, explicitly set the customer: enrollment ownership is not copied into imported device records.
Status
Where each platform stands today.
APPLE IOS, IPADOS AND MACOS
Mac inventory and profiles observed.
Needs: an APNs MDM certificate with its matching private key and topic. Implemented: manual enrollment, passcode/restriction/Wi-Fi profiles, refresh, lock and erase; macOS also has an agent permission profile. The current deployment check found a managed Mac with acknowledged inventory/profile commands. That does not verify iPhone/iPad enrollment, lock or erase on every device.
ANDROID ENTERPRISE
Integration implemented; customer path unverified.
Needs: an authorized Google service account and bound enterprise. Implemented: code/QR enrollment, AMAPI policies, inventory sync, lock, reboot and wipe requests. No Google binding or enrolled Android device was found in the active workspaces inspected. Verify an authorized device before relying on this for a customer fleet.
How it works
From an email to a managed device.
01
Create the enrollment
Choose the customer and platform, with an optional policy. Apple devices can inherit that customer; Android imports need an explicit customer assignment after sync.
02
Send it
Email the user an enrollment link, or hand them a QR code. The landing page walks them through it.
03
Verify enrollment and policy
Apple queues its selected configuration profile after push-token enrollment. Android receives the selected Google policy, or the default reporting policy when none is selected. Verify the device outcome rather than assuming every starter template applies automatically.
04
It appears where it should
Check inventory, customer assignment and portal visibility. An enrollment link, sent email or locally stored policy is not proof that setup completed.
Limits
What it does not do yet.
Enrollment and offboarding boundaries
- Windows and Linux use the desktop agent; there is no Windows/Linux MDM enrollment provider in this screen. Separately, the Microsoft hub can request actions on devices already managed by external Microsoft Intune, including Windows.
- Apple MDM and the Mac agent are separate enrollments. Screen Recording still needs local approval.
- Retire changes local state and blocks the Apple command channel while Retired; it does not remove management or profiles from the device.
- Local enrollment revocation does not revoke a Google-issued token and can stop existing Apple management communication. Verify offboarding separately.
Not in the product today: one connected asset record across agent, network, mobile and manual sources, and verified offboarding.
Questions
Good to know.
Your APNs MDM push certificate, matching private key and topic. RMM accepts the existing PEM material; it does not generate or sign the push certificate request. Configuration acceptance still needs verification on the device.
An authorized Google service account and bound enterprise. Enrollment requires a real Google-issued code; stored settings alone do not verify the connection or device setup.
The current active-workspace check found no Google binding or Android devices. Runtime source is deployed, but a Google-backed customer path was not verified. Talk to us before relying on it for a fleet.
The App requests Apple lock/erase and Android lock/reboot/wipe. Delivery requires the configured provider and a reachable, compatible enrolled device. Confirm the actual outcome; a sent or queued message is not completion.
Assigned, non-retired MDM devices appear read-only under Mobile devices. Explicitly assign the customer after Android sync; the import does not inherit it from the enrollment.
Keep exploring
Limits, checked daily
Not in the product today.
Each line below is a gap recorded against this capability in the product's own feature record. A line leaves this page by itself on the next daily run once that record says the gap is closed, so the list cannot fall behind what we ship. The rest of this page is written by hand.
- There is no lost mode that tracks the location of a missing device.
- Apple devices enroll, take profiles and can be locked, wiped and erased; automated device enrollment, managed app purchasing, disk encryption through management and kiosk modes are not built yet.
- Android devices take policies and can be locked, restarted and wiped; kiosk mode, location and remote viewing are not built yet.
Next step
Tell us about your customers' device mix.
Half an hour on a call. We will walk through enrollment and management for the devices you actually support.