

Microsoft 365
Microsoft 365 posture and Intune management
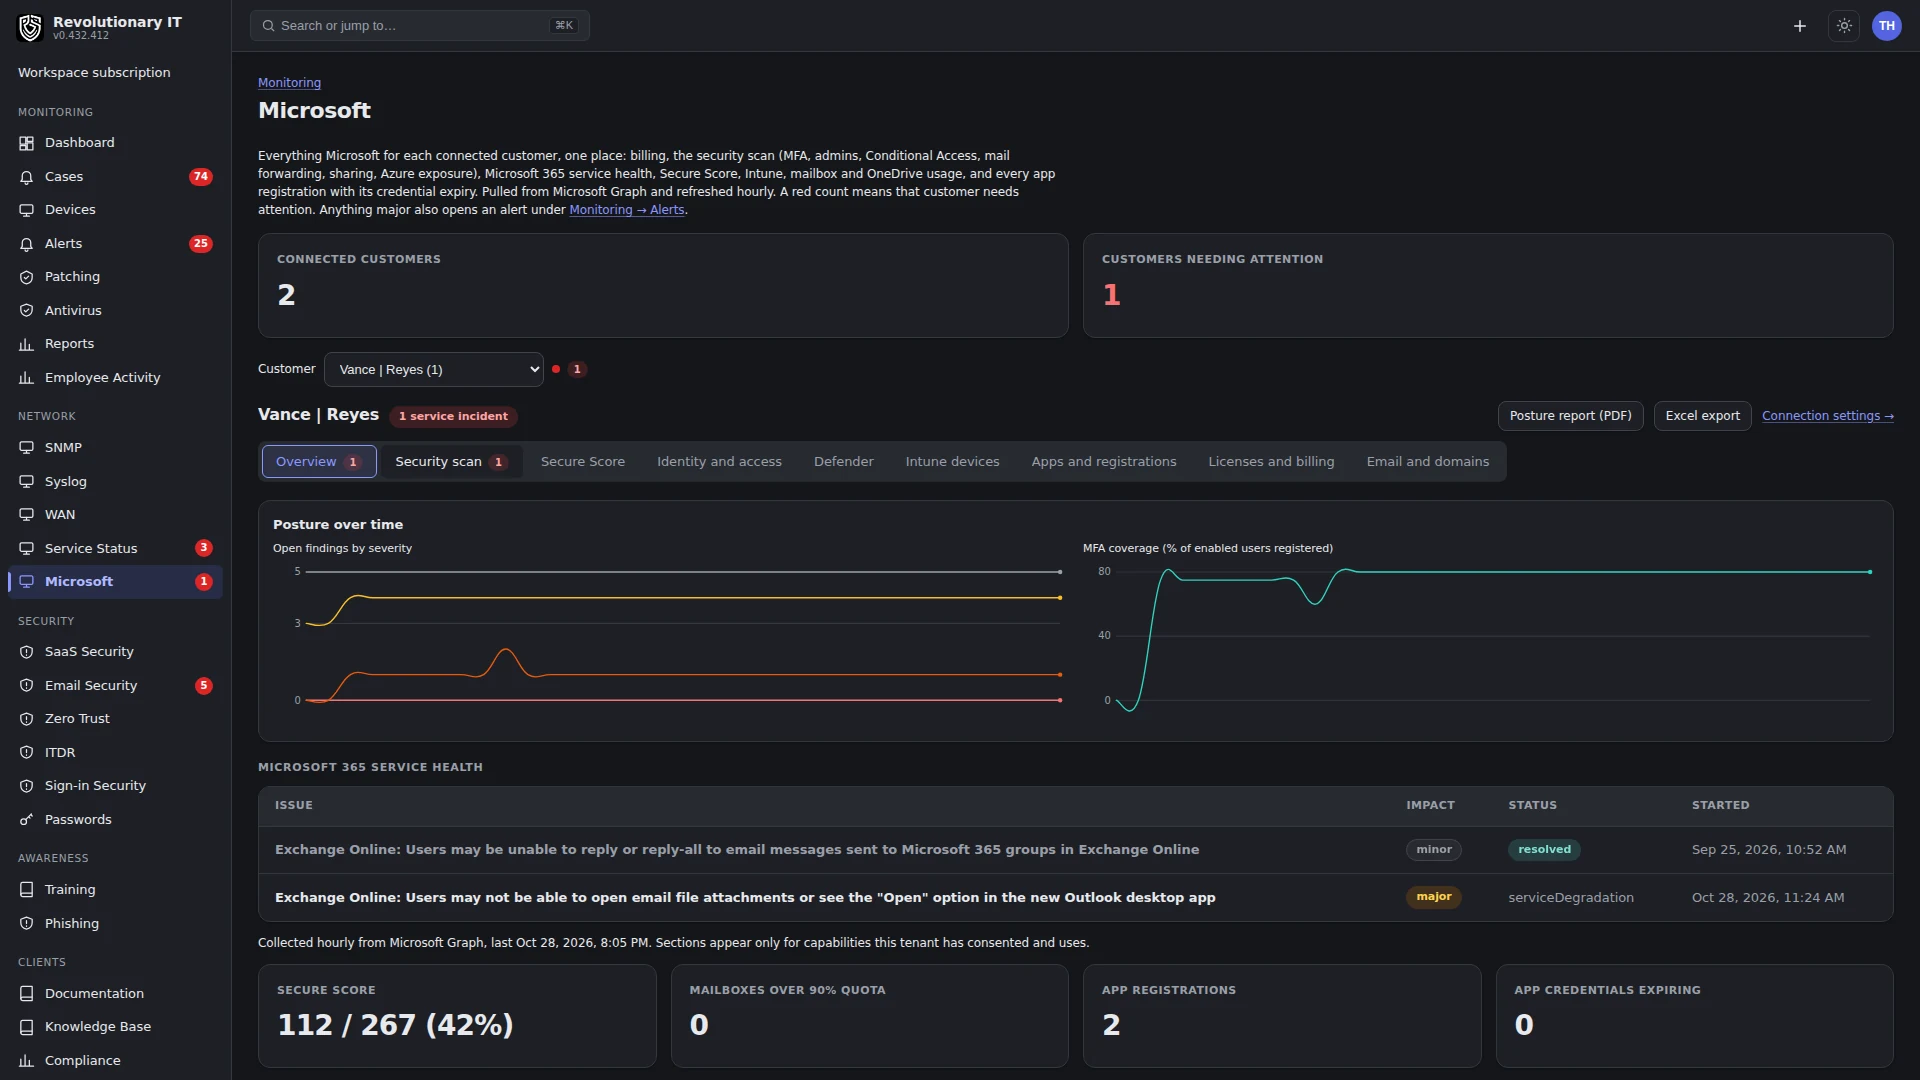
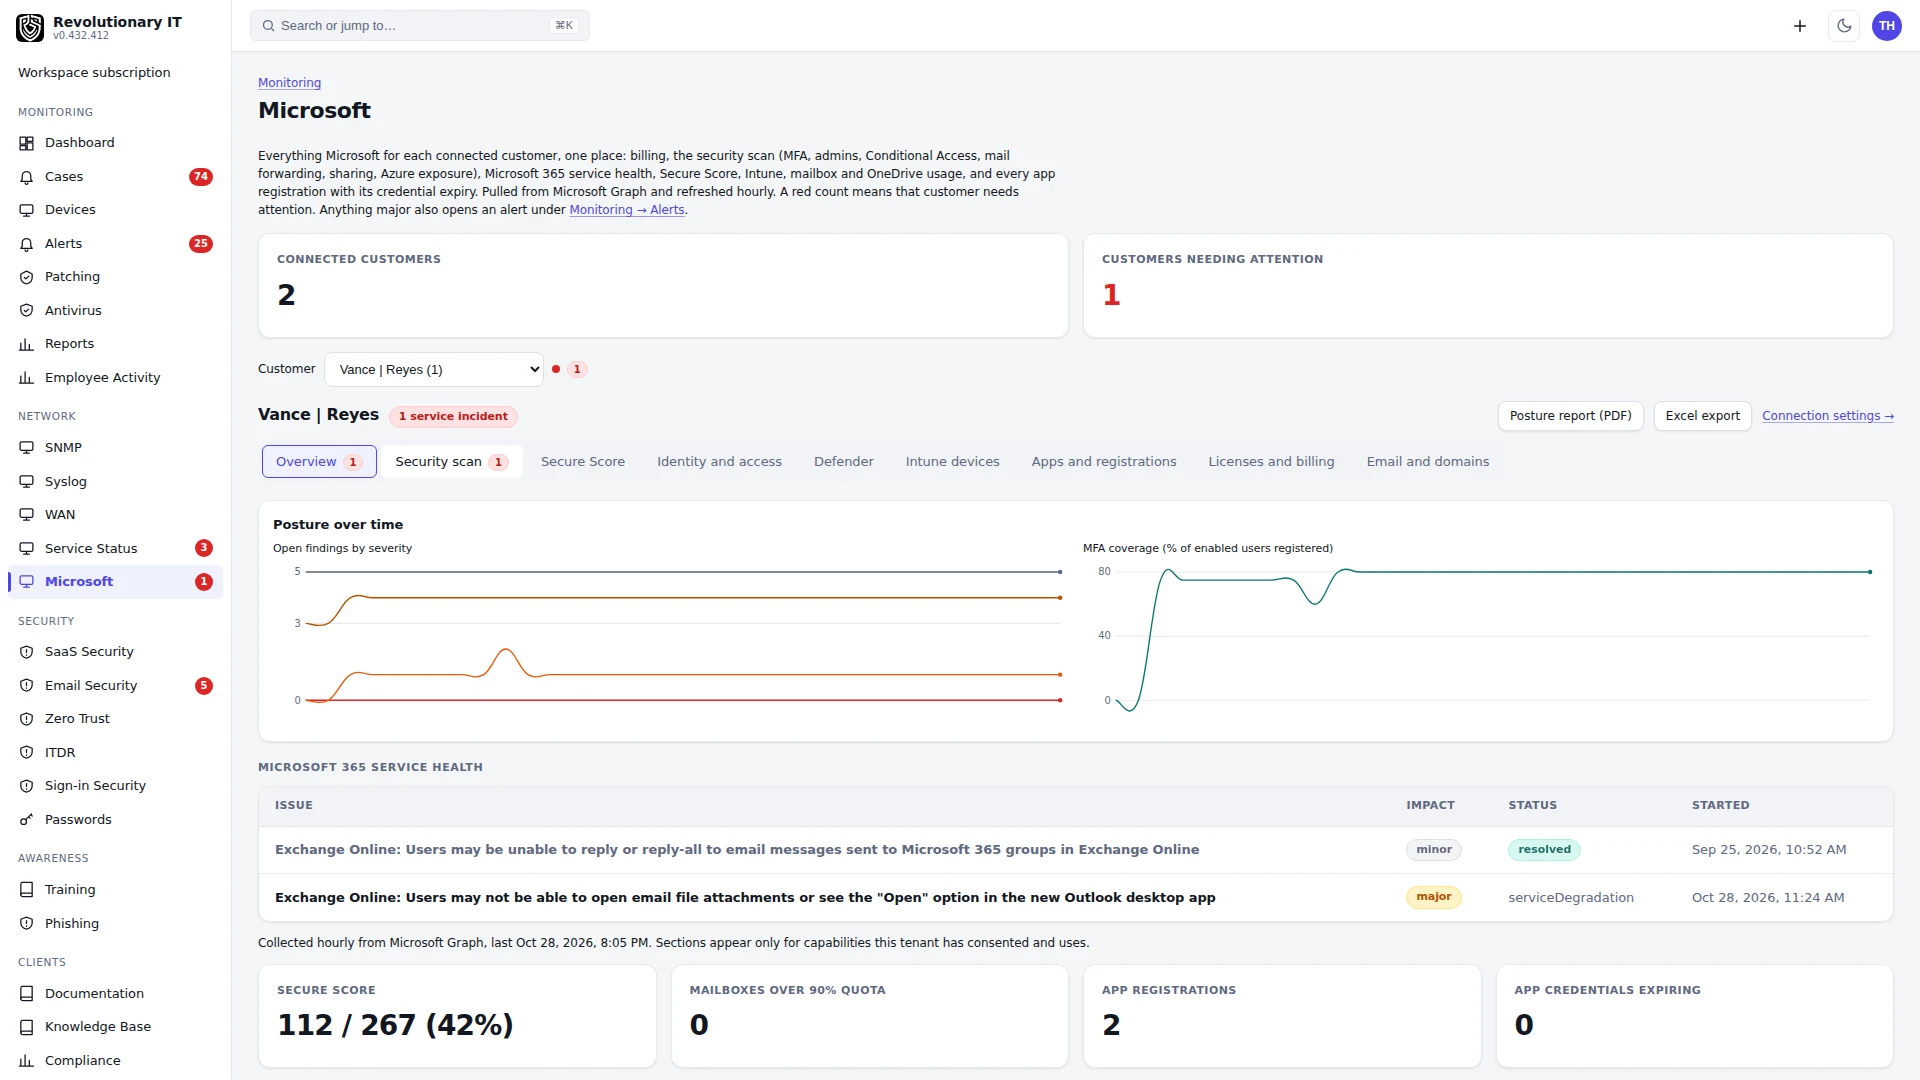
The tenant is half the estate. See each customer's Microsoft 365 security posture over time, the licenses paid for and not used, the apps that hold access, and the Intune devices you can act on, all from the same workspace as their endpoints.
Posture
Trends, not a one-off audit.
01
Secure Score over time
Ninety days of history charted, with Microsoft's improvement actions ranked by the points still available.
02
Findings with a framework
Findings carry CIS Microsoft 365 Benchmark and NIST CSF references, and Essential Eight where one applies, so they mean something to an auditor.
03
License waste
Assigned against purchased, per SKU, and a finding when paid licenses sit on disabled accounts.
04
Connected applications
Every third-party application holding a grant, with broad mail, file and directory access called out, and AI tools identified separately.
05
Mail domain authentication
SPF, DKIM and DMARC checked by live DNS lookup for every verified domain on the tenant.
06
Consent and guests
User consent settings, application registration rights, guest invitation policy, self-service password reset and the administrator approval workflow.
How it works
Read first. Act where you choose to.
01
1. The customer approves one application
The customer's administrator approves one Revolutionary RMM application for their tenant. Posture, licensing, applications, domains and consent are then read through the Microsoft Graph API.
02
2. Findings arrive with their references
Each finding carries its framework references and tells you what to change and where.
03
3. Act on devices in Intune
Devices already managed by Microsoft Intune are listed with model, serial and encryption state. Optional write scopes enable sync, lock, restart, retire, wipe and delete requests; disable/enable affects the matched Entra device account. Compatibility and actual provider/device outcomes must be verified.
04
4. Change settings through a plan
Hardening change plans cover a set of tenant settings, such as security defaults, sharing and user consent. Each plan shows the exact before and after values. A change applies only after approval, is read back to confirm it took, and comes with a rollback proposal.
05
5. Hand the customer a report
Posture exports to a white-labeled PDF and a spreadsheet, both carrying the framework summary, so the review meeting has a document rather than a screen share.
The detail
Safeguards on the write paths.
Confirm
Typed confirmation
Destructive Intune actions need you to type the device name, and a wipe needs the word typed in full.
Audit
Every action on the record
The action path attempts to record its result. Verify the returned provider status, audit evidence and native outcome separately.
Permissions
Missing access is named
Inspect per-check denied/error status and timestamps. Missing or stale data does not establish a healthy tenant; some permission errors name the required scope.
Billing
Subscription health
Tenant subscriptions are checked hourly. A real payment failure or suspension raises an alert, and a superseded subscription aging out beside its replacement is recognized instead of crying wolf.
Identity
Account containment
Blocking a sign-in and revoking sessions, by hand or by a rule you turn on, are covered on the identity security page.
Scope
Optional write paths
The write paths are Intune device actions, identity containment and hardening change plans. Each one is optional.
Limits
What this is and is not.
Limits
- It is not a replacement for Microsoft's admin centers. Settings outside the hardening change plans are changed in Microsoft's own tools, and findings tell you what to change and where.
- Hardening changes never apply in one click. Each one needs approval first.
- Intune actions reach only devices enrolled in the customer's Intune.
Not in the product today: verified offboarding across accounts and devices, and customer-facing outcome reports.
Questions
Good to know.
The customer's administrator approves one Revolutionary RMM application for their tenant. Each customer approves separately, so each one can see exactly what you are allowed to read and change.
For the settings covered by hardening change plans, yes, after approval. Each plan shows the exact before and after values, reads the result back to confirm it, and proposes a rollback. Everything else you change in Microsoft's admin centers, guided by the finding.
The platform names the missing Microsoft Graph permission instead of failing quietly, so you know exactly what the customer's administrator needs to grant.
A white-labeled PDF and a spreadsheet of their posture, both with the framework summary.
CIS Microsoft 365 Benchmark and NIST CSF, plus Essential Eight where one applies. Findings carry the references that apply to them.
Keep exploring
Limits, checked daily
Not in the product today.
Each line below is a gap recorded against this capability in the product's own feature record. A line leaves this page by itself on the next daily run once that record says the gap is closed, so the list cannot fall behind what we ship. The rest of this page is written by hand.
- Posture collection does not automatically remediate findings. The supported Microsoft hardening settings have separate reviewed change plans; other settings require the tenant's admin tools.
- A hardening change plan covers a set of tenant settings for one customer; applying one agreed configuration across every customer's tenant, and holding each of them to it, is not built yet.
- Release and sender blocking depend on the connected email-gateway adapter; this Microsoft Defender adapter does not implement them. Cross-mailbox removal of delivered messages and automatic forwarding-rule remediation are not implemented here.
Next step
Review a tenant together.
Half an hour on a call. We will walk through posture, license waste and an Intune action.